Decloak - Web security intelligence Reviews — Discover what people think of this product.

Decloak - Web security intelligence
Security intelligence for teams from vibe coders to enterprise
What users think of Decloak - Web security intelligence
Maker
-
Supporters
-Idea
0.0
Product
0.0
Feedback
0
Roasted
0
More about Decloak - Web security intelligence
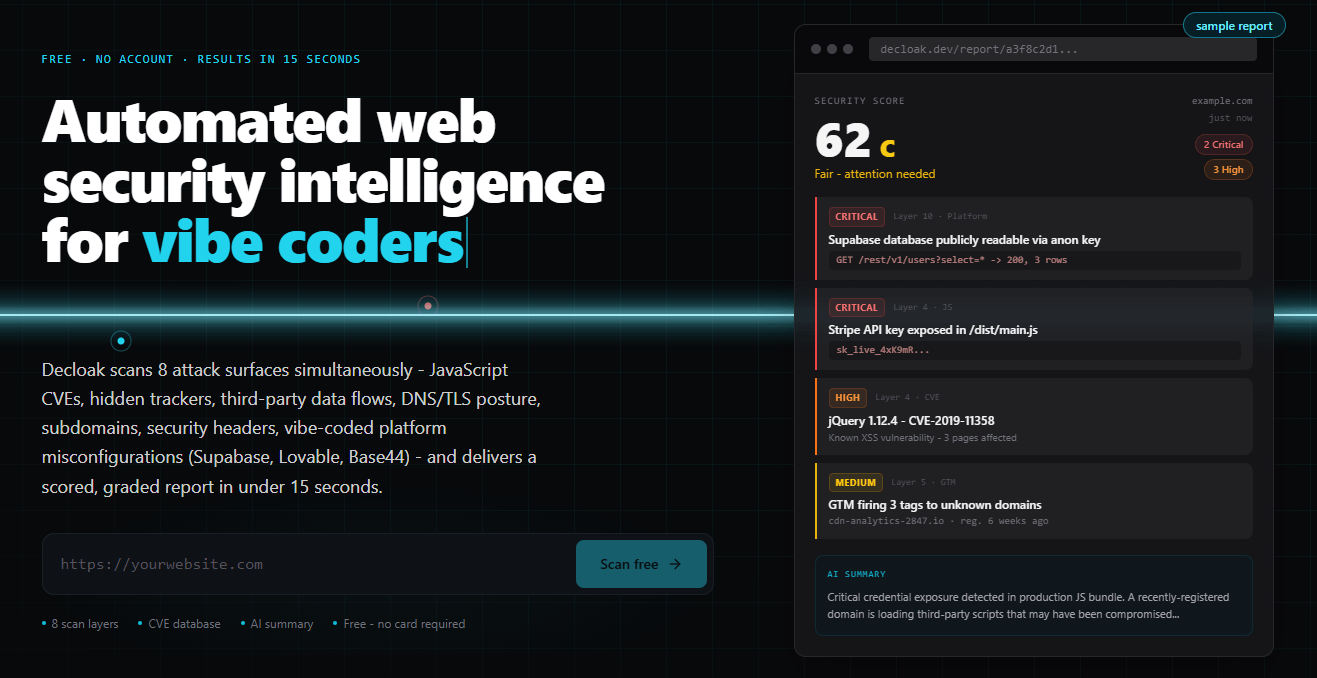
Vibe coding gets you from idea to live app in hours, but the security review is usually the first thing that gets skipped. Decloak is built to catch what shipping fast leaves behind.
Paste a URL and Decloak automatically fingerprints your platform (Lovable, Supabase, Base44, Bubble, Next.js) and checks for the misconfigurations known to affect each one, most commonly a Supabase database left publicly readable because Row Level Security was never turned on. It also flags exposed API keys in client-side JS, vulnerable libraries, missing security headers, and hidden trackers, across a full 8-layer scan that correlates findings instead of checking each one in isolation.
Beyond the initial scan, Decloak's AI agent investigates rather than running a fixed checklist: it follows threads across your whole site, reconstructs exposed source code from source maps, and cross-references suspicious domains against threat intel. Enterprise plans add AI-powered penetration testing (sandboxed sqlmap, nuclei, and jwt_tool runs confirming real exploitability) and compliance mapping to SOC2, ISO 27001, NIS2, and DORA, with exportable audit evidence.
Built by a solo founder who's spent 25 years in code intelligence and governance tooling, and got tired of watching security get skipped every time speed won.
Tags
Product Categories
Featured Today
tiun
Payments backend for indie hackers
All-in-one: Auth, payments & DB
Single command: MCP, Skills
Built for developers.
Merchant of Record. Better fees.
The Weekly Top 10 in your inbox
Best launches + founder deals.