This task can be performed using Decloak - Web security intelligence
Security intelligence for teams from vibe coders to enterprise
Scan vibe-coded sites before release
This workflow is for vibe coding teams shipping live apps quickly, especially projects built with Lovable, Supabase, or Base44. It is triggered before launch, after major changes, or whenever a new dependency, database rule, or API integration reaches a public URL.
Effective web security scanning starts with the live URL, checks secrets, database exposure, libraries, and application behavior, then routes findings to an owner for remediation and retesting. A good outcome is a release with critical exposures resolved and a clear record of remaining risk.
Best product for this task
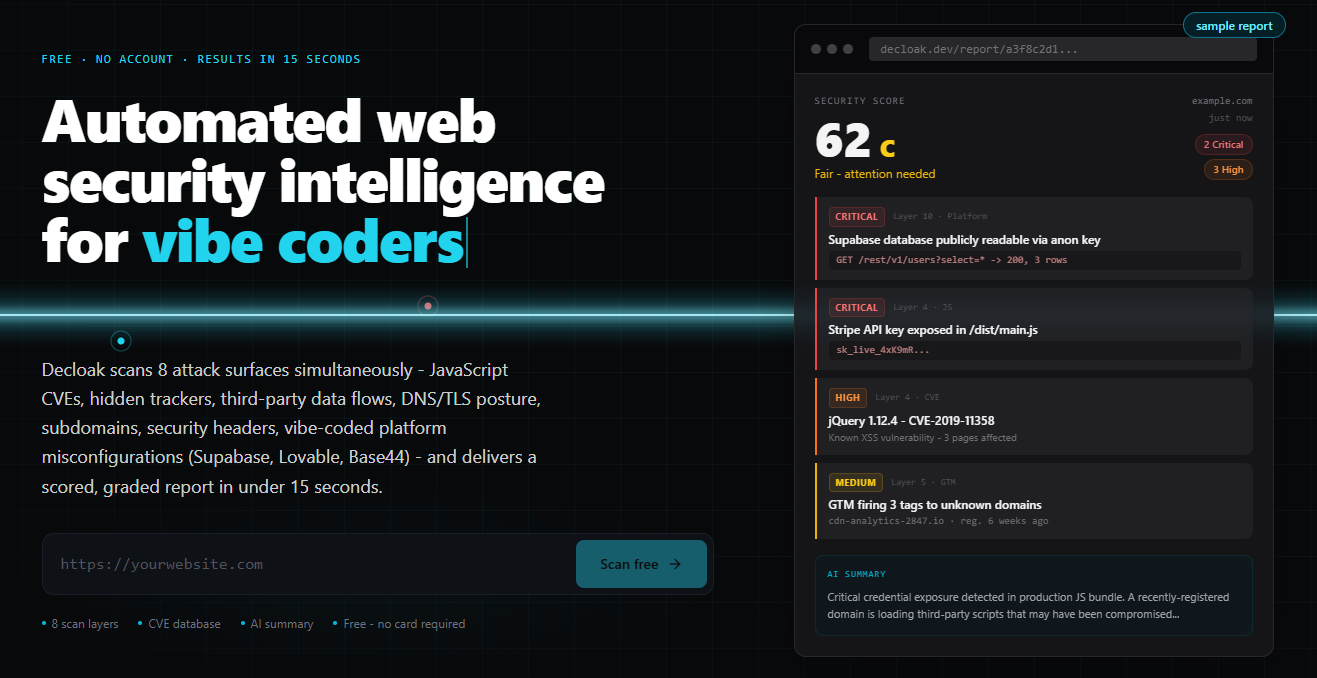
Decloak scans any live URL across 8 layers, catching exposed API keys, misconfigured databases, and vulnerable libraries, including the specific failures common to apps built with Lovable, Supabase, and Base44. Paid tiers deploy an AI agent that investigates a whole site, run AI-powered penetration testing, and map findings to SOC2, ISO 27001, NIS2, and DORA controls, all for a fraction of what tools like AppCheck or Qualys cost.
What to expect from an ideal product
- Multi-layer scanning of any live URL
- Detection of exposed keys, databases, and vulnerable libraries
- Coverage for Lovable, Supabase, and Base44 failures
- AI investigation and penetration testing options
- Control mapping for major compliance frameworks
More about release gates
Treat scanning as a release control, not a one-off audit. Define who reviews findings, what blocks deployment, and how verified fixes return to the release queue.
- Scan the live preview or production URL after every material deployment.
- Block releases for exposed secrets, public databases, and critical vulnerable libraries. Assign an owner and retest each fix.
- Schedule penetration testing for major feature or authentication changes, then track recurring findings separately.