This task can be performed using Decloak - Web security intelligence
Security intelligence for teams from vibe coders to enterprise
Map findings to controls
Start by normalizing web security findings into a consistent record: affected asset, weakness, severity, exploitability, evidence, and remediation. Then identify the applicable SOC 2 Trust Services Criteria and ISO 27001:2022 Annex A control objectives.
Map the underlying risk and required process, not the scanner label alone. For each relationship, record the control, rationale, owner, supporting artifact, remediation status, and retest date. Flag weak or unmapped relationships for review by the control owner or auditor.
Best product for this task
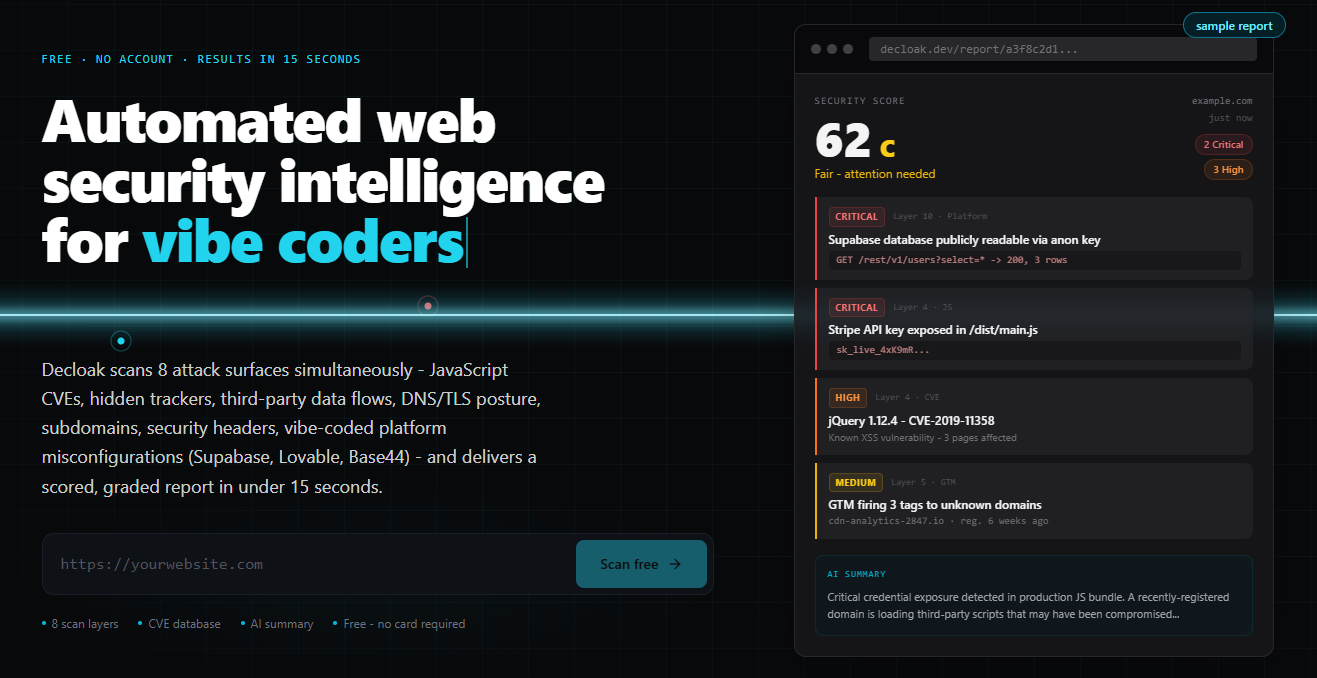
Decloak scans any live URL across 8 layers, catching exposed API keys, misconfigured databases, and vulnerable libraries, including the specific failures common to apps built with Lovable, Supabase, and Base44. Paid tiers deploy an AI agent that investigates a whole site, run AI-powered penetration testing, and map findings to SOC2, ISO 27001, NIS2, and DORA controls, all for a fraction of what tools like AppCheck or Qualys cost.
What to expect from an ideal product
- Maps findings to current SOC 2 and ISO 27001 controls
- Preserves affected assets, timestamps, and raw evidence
- Explains mapping rationale and confidence
- Tracks remediation ownership and retest status
- Exports traceable records for audit review
More about mapping confidence
Treat every automated crosswalk as a hypothesis. Strong compliance evidence links the finding, affected asset, control objective, remediation, and retest result through one traceable record.
- Mark mappings direct when the finding clearly tests a control objective.
- Label risk indicators as indirect rather than claiming full control failure.
- Leave findings unmapped when no defensible relationship exists.