This task can be performed using Decloak - Web security intelligence
Security intelligence for teams from vibe coders to enterprise
Test AI-built websites safely
AI website penetration testing is for founders, vibe coders, security teams, and enterprises assessing a live app before launch, after rapid changes, or when moving beyond lightweight scanners. It should uncover issues across code, infrastructure, data access, and dependencies.
A useful workflow starts with a URL, investigates reachable pages and services, verifies exposed secrets, database misconfigurations, and vulnerable libraries, then prioritizes remediation. A good result is reproducible evidence, fewer critical exposures, and clear control mappings for audit work.
Best product for this task
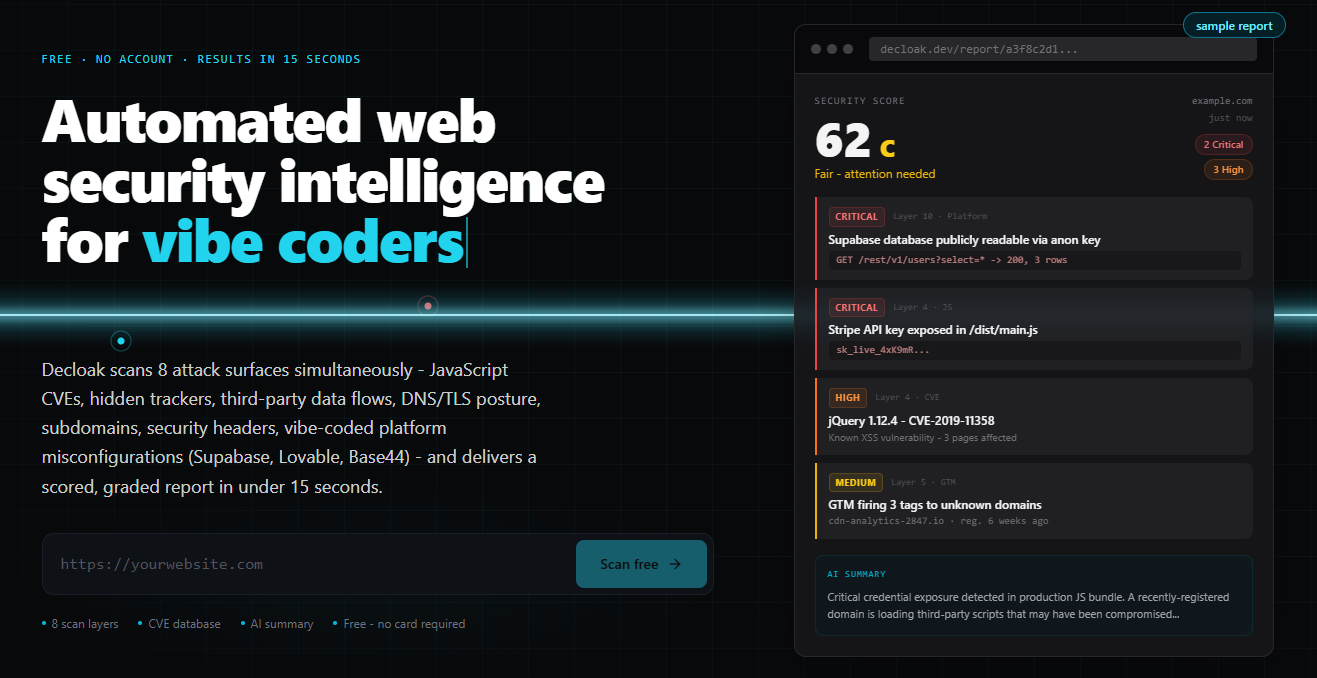
Decloak scans any live URL across 8 layers, catching exposed API keys, misconfigured databases, and vulnerable libraries, including the specific failures common to apps built with Lovable, Supabase, and Base44. Paid tiers deploy an AI agent that investigates a whole site, run AI-powered penetration testing, and map findings to SOC2, ISO 27001, NIS2, and DORA controls, all for a fraction of what tools like AppCheck or Qualys cost.
What to expect from an ideal product
- Eight-layer scanning from any live URL
- Detection of exposed keys, database issues, and vulnerable libraries
- Coverage for Lovable, Supabase, and Base44 failure modes
- Whole-site investigation by an AI agent
- Findings mapped to major security frameworks
More about evaluation testing
Run a short comparison against a staging or approved production URL. Score detection quality, investigation depth, remediation clarity, and whether compliance mapping uses findings your team can verify.
- Seed known test issues, such as a disposable API key and outdated library, then compare detection and false positives.
- Check whether whole-site investigation covers reachable pages rather than only the submitted page.
- Measure time from scan start to a verified, assigned remediation task.